


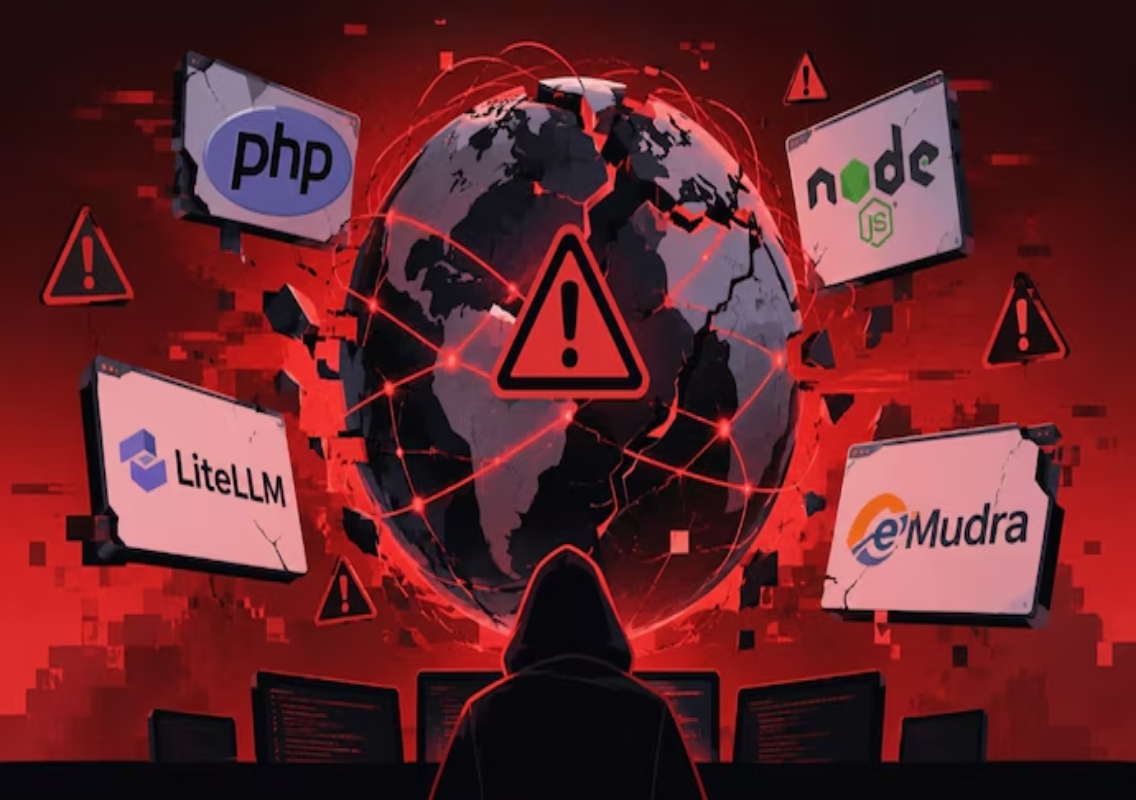
New Delhi: A series of cybersecurity incidents has put internet infrastructure, software developers and technology companies on high alert, following the discovery of critical vulnerabilities in PHP, weak digital certificate keys linked to Indian firm eMudhra, and security compromises affecting AI development and cloud platforms.
The developments reported on October 21 and 22, 2026, include urgent software patches, browser security measures, investigations into possible data exposure and warnings about AI-assisted cyberattacks. Together, they underline the risks facing organisations that depend on interconnected software systems, cloud services and digital authentication technologies.
The incidents involve separate vulnerabilities and security investigations, rather than evidence of one coordinated attack against the internet. However, their near-simultaneous emergence has raised concerns about the security of widely used technologies and the speed at which weaknesses can affect organisations worldwide.
Critical PHP vulnerabilities trigger urgent warnings
PHP, a server-side programming language widely used to build websites and web applications, became a major focus after two critical security vulnerabilities were disclosed. The flaws, collectively referred to in reports as PHP2Shell, could allow unauthenticated attackers to execute malicious code on vulnerable servers.
The vulnerabilities were assigned the identifiers CVE-2026-109618 and CVE-2026-109619. Their severity was rated 9.2 out of 10, placing them in the critical category.
PHP is used across a substantial proportion of websites, including platforms built on popular content management systems. A vulnerability in the underlying programming language can therefore affect more than an individual website or application.
India’s Computer Emergency Response Team (CERT-In) issued a warning about the flaws, while US cybersecurity agencies also urged organisations to take immediate action. The PHP project released security updates on October 21, 2026, and recommended that administrators upgrade affected installations.
Organisations unable to apply the fixes immediately were advised to consider taking vulnerable systems offline until they could be secured. Some website operators reportedly took precautionary measures while assessing their exposure.
The incident also drew attention to the role of artificial intelligence in cybersecurity research. Reports said an AI model helped identify the vulnerabilities, illustrating how AI tools can assist in finding flaws in widely deployed software. Such capabilities can support defensive security research, although similar tools may also be used by attackers.
eMudhra certificate flaw raises global trust concerns
Bengaluru-based eMudhra faced a separate cybersecurity issue after researchers discovered dangerously weak cryptographic private keys associated with eight intermediate certificate authority certificates.
Digital certificates help browsers and other software verify the identity of websites. They are an important part of the system that establishes trusted, encrypted connections between users and online services.
The affected eMudhra keys had been generated with insufficient randomness, making them recoverable. A malicious actor possessing the relevant private keys could potentially create fraudulent certificates and impersonate websites to systems that continued to trust them.
The incident prompted major technology companies, including Apple, Google and Mozilla, to block the affected certificates in their browser trust systems. Cloudflare also deployed emergency measures to address the risk.
CERT-In issued an advisory covering the compromised intermediate certificates. The Ministry of Electronics and Information Technology (MeitY) also constituted a special team to investigate the incident and coordinate with relevant stakeholders.
The government said the impact on Indian websites and applications had been limited and short-lived. It also clarified that eMudhra’s regulated Digital Signature Certificate and eSign services remained unaffected because the incident concerned its separate international website-security certificate business.
The episode demonstrates how a weakness in a certificate authority can have implications beyond the company that issued the certificates. Browser developers, operating system providers, website operators and organisations maintaining their own trust stores may all need to respond to ensure that affected certificates are no longer accepted.
Node.js releases security updates
Node.js, an open-source runtime that allows JavaScript to run outside web browsers, also issued security updates during the same period.
The updates addressed four high-severity vulnerabilities. One could potentially permit remote code execution, while two others affected Transport Layer Security (TLS) certificate verification and could allow attackers to bypass checks intended to establish whether a server’s identity should be trusted.
The security releases also introduced an updated certificate store designed to block the compromised eMudhra certificates and other identified certificates.
The connection between the two developments is important: even when a certificate authority’s weakness is identified, applications and server environments must have the appropriate fixes and trust-store updates to stop accepting affected certificates.
Developers and system administrators were advised to install the latest security releases available for their supported Node.js versions. Organisations operating older versions were urged to move to supported releases and review their certificate-handling arrangements.
LiteLLM compromise exposes AI software supply-chain risks
Another incident involved LiteLLM, an open-source proxy that helps applications route requests to different large language model providers.
According to security reporting, malicious code was inserted into compromised LiteLLM releases. The code could potentially collect system information, browser data, developer secrets, cloud credentials and authentication files used by AI tools.
Researchers at cybersecurity company Wiz said the malware used Python startup hooks, meaning it could be triggered when Python launched rather than only when a developer deliberately imported or opened LiteLLM.
This approach creates a significant risk for development environments. A developer may unknowingly install a compromised package and expose credentials belonging to several systems, potentially allowing attackers to move beyond a single application.
LiteLLM said it had removed the malicious releases and images and provided remediation guidance for affected users. The incident also renewed attention to software supply-chain security, in which attackers target trusted packages, dependencies or update mechanisms to reach a wider group of users.
Organisations using affected versions should follow the project’s official instructions, investigate their environments and rotate potentially exposed credentials. Simply uninstalling a package may not be sufficient if secrets have already been accessed.
Railway investigates possible customer data exposure
Cloud platform Railway also reported anomalous activity involving systems that stored customer environment variables. Its investigation indicated that an unauthorised third party may have obtained the decrypted contents of some of these variables.
Environment variables are commonly used to store sensitive configuration information, including database credentials, API keys, access tokens and other secrets required by applications.
If exposed, these details could allow attackers to access connected services or impersonate authorised applications. The potential impact depends on which variables were affected and whether the associated credentials remained valid.
Railway advised customers to rotate stored environment variables and API keys, review service logs and examine systems for unusual activity. It also reported taking steps to reset certain credentials as part of its response.
The company said its initial assessment suggested that the incident could affect a subset of users. However, the possibility of credential exposure makes it important for customers to investigate their own deployments rather than assume that no action is required.
Microsoft warns of AI-assisted cyberattacks
Microsoft separately disclosed details of a campaign associated with a China-linked hacking group it tracks as Storm-0940.
According to Microsoft’s findings, the group used an AI-powered tool known as ARTEX to automate aspects of cyberattacks targeting organisations worldwide. The campaign involved the abuse of trusted digital credentials connected to ConnectWise’s Cloud Backup service to gain access to Microsoft 365 environments.
The reported activity demonstrated how attackers can exploit trusted relationships between software providers and their customers. Rather than attacking each organisation independently, a compromise involving a service provider or its credentials can potentially provide a route into multiple customer environments.
Microsoft reported that the campaign targeted organisations across sectors including government, finance, manufacturing, technology, defence and energy.
Organisations using or previously using the affected service were advised to follow official security guidance, review Microsoft 365 sign-in records and check for suspicious administrator activity. Security teams were also encouraged to preserve evidence for investigation instead of deleting potentially affected applications without assessing the consequences.
The findings add to concerns that AI-assisted tools can help attackers automate reconnaissance and other parts of an intrusion. They do not mean that every AI tool or AI service is inherently unsafe, but they highlight the need for stronger identity controls, monitoring and incident-response procedures.
What organisations and users should do
The incidents highlight several practical steps for improving cybersecurity.
- Install security updates: Administrators should patch affected PHP and Node.js installations using official releases and verify that updates have been applied correctly.
- Update browsers and operating systems: Current versions are better positioned to recognise revoked or distrusted certificates and address known security issues.
- Rotate exposed credentials: Organisations that may have been affected by the LiteLLM or Railway incidents should follow official remediation guidance and replace potentially compromised keys, tokens and passwords.
- Review access logs: Unusual sign-ins, unexpected administrator privileges and unfamiliar system activity can help identify possible unauthorised access.
- Secure software dependencies: Development teams should verify package versions, monitor security advisories and limit the privileges available to build and deployment environments.
- Follow official advisories: Organisations should rely on CERT-In, software maintainers and affected service providers for the latest technical instructions.
Individual users should keep their browsers and devices updated and remain alert to suspicious websites and unexpected authentication requests. Organisations, meanwhile, need to treat certificate trust, software dependencies and cloud credentials as connected parts of their security infrastructure.
A warning about interconnected digital systems
The cybersecurity developments reported over the two days illustrate the range of weaknesses that can put digital systems at risk. A flaw in a programming language can threaten web servers, compromised certificate keys can undermine website authentication, and malicious software packages can expose the credentials used throughout an organisation.
The incidents do not establish that the entire internet has been compromised. They do, however, show how quickly separate vulnerabilities can demand urgent action from developers, technology companies and government agencies.
As organisations adopt more cloud services and AI-powered development tools, maintaining secure software, managing credentials carefully and responding promptly to verified security advisories will remain essential to protecting digital infrastructure.