


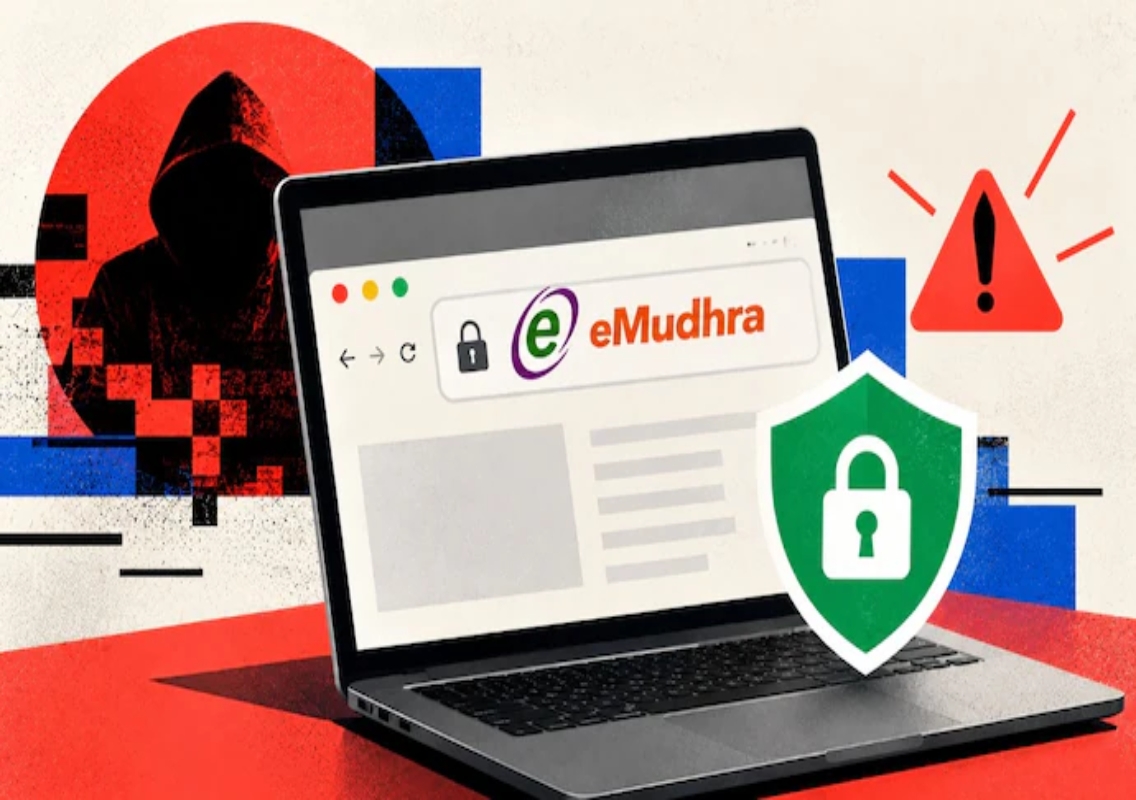
Bengaluru: Digital security company eMudhra has decided to withdraw from the global SSL/TLS certificate business following a security incident involving weak cryptographic keys, with the company citing rising compliance costs, operational complexity and intense social media scrutiny surrounding the issue.
The Bengaluru-based company announced the decision on October 22, 2026, after eight intermediate certificate authorities associated with its international website-security operations were found to have weak private keys. The discovery prompted major technology companies, including Google, Apple, Microsoft and Mozilla, to distrust or block the affected certificates.
eMudhra said the global SSL/TLS certificate business accounts for around 1% of its overall revenue. It argued that the attention generated by the incident, particularly through social media, was disproportionate to the size of the business segment.
The company has maintained that its infrastructure was not compromised and that no customer data was breached. It has also clarified that its Indian digital signature certificate (DSC) and eSign services remain unaffected.
The decision marks a significant change for eMudhra’s international website-authentication operations, which form part of the broader digital trust ecosystem used to secure online communications. It also highlights the reputational consequences that cybersecurity incidents can have for companies responsible for technologies underpinning internet security.
Why eMudhra is exiting the global certificate business
In its announcement, eMudhra said that the global SSL/TLS certificate segment had become increasingly complex and expensive to operate. Rising data-sovereignty requirements, compliance obligations and the cost of maintaining certificate infrastructure have added to the challenges.
The company also pointed to the availability of free SSL/TLS certificates from large providers, which has reduced the commercial attractiveness of the business.
The security incident appears to have accelerated the decision. According to the company, the level of scrutiny generated by social media discussion was disproportionate to the segment’s contribution to its overall operations.
However, the withdrawal follows a technical issue that raised legitimate questions about the reliability of the affected certificates. The episode attracted attention because digital certificates are an important part of the system browsers use to verify website identities and establish encrypted connections.
The company’s decision therefore reflects a combination of commercial considerations, compliance pressures and reputational concerns following the incident.
What went wrong with eMudhra’s certificates?
The incident involved eight intermediate certificate authorities used in eMudhra’s international public key infrastructure. These authorities help issue digital certificates that browsers and other software can trust.
According to eMudhra’s statement, a flaw during a key-generation ceremony in April 2025 resulted in a second set of weak private keys being created alongside the intended strong keys. The weak keys were subsequently published to browser trust stores.
The issue was discovered by an independent security researcher in October 2026. The researcher reported the findings to major browser and technology companies, triggering an investigation and emergency security measures.
India’s Computer Emergency Response Team (CERT-In) issued an advisory on October 21. It warned that attackers who recovered the affected private keys could potentially create fraudulent certificates and impersonate legitimate websites, with risks including interception or modification of communications under certain conditions.
The problem was not a general failure of the underlying elliptic-curve cryptography algorithm. Instead, CERT-In said the weakness arose from insufficient randomness in the generation of the affected keys.
The distinction matters because it identifies the key-generation process, rather than the cryptographic algorithm itself, as the source of the vulnerability.
Google, Apple and Mozilla respond
The discovery led major technology companies to take steps to prevent the affected certificates from being trusted by their products.
Google updated protections for Chrome and Android users, while other browser and operating system providers also moved to distrust the affected certificate authorities. These actions were intended to prevent the weak keys from being used to establish trusted connections through the affected certificate chains.
The incident demonstrates how the security of the internet depends on a network of certificate authorities, browser developers, operating system providers and website operators. A weakness at one certificate authority can require action from several companies to reduce the risk to users.
eMudhra said it revoked the affected certificate authorities within 14 hours of discovering the issue and began working with browser programmes and customers on remediation.
The company has also committed to completing its remaining obligations to browser root programmes, including providing a comprehensive report on the root cause of the incident.
Were websites or customer data compromised?
eMudhra has stated that its infrastructure was not compromised and that no data was breached. It also said that no end-entity certificates had been issued by the affected intermediate certificate authorities.
The company’s statement indicated that only one of the affected intermediates had been deployed in production. These details are important when assessing the incident’s potential scope.
However, weak private keys can create serious risks even when there is no evidence of a conventional network intrusion. If an attacker can recover a certificate authority’s private key, it may become possible to issue fraudulent certificates that could be trusted by systems that have not yet blocked the affected authority.
CERT-In’s advisory outlined the potential risks, while eMudhra said the affected certificates had been withdrawn and its infrastructure remained secure.
The incident should therefore be understood as a cryptographic key-generation failure with potential security implications, rather than confirmed evidence that customer databases were breached or that users’ private information was stolen.
Indian digital signature and eSign services remain unaffected
eMudhra has emphasised that the international TLS certificate business operates separately from its regulated Indian digital signature certificate and eSign operations.
Digital signature certificates are used to authenticate individuals and organisations and support activities such as digitally signing documents and completing online transactions. TLS certificates, by contrast, help browsers verify websites and secure communications between clients and servers.
The company said its Indian DSC and eSign services continue to operate normally and are not affected by the international certificate incident.
CERT-In’s advisory also distinguished the two business areas, noting that the reported issue concerned eMudhra’s global website-security certificate operations rather than its regulated Indian digital-signature services.
The distinction is particularly relevant for businesses and individuals who use digital signatures for official transactions. They should follow communications from eMudhra and relevant authorities rather than assume that all of the company’s services have been affected.
What happens to existing certificate customers?
eMudhra said it would coordinate with customers and browser programmes to support a transition away from its global SSL/TLS certificate business.
The company has indicated that it will help affected customers obtain replacement certificates through its partners. Certificate revocation and status services will continue until issued certificates have expired or been replaced, according to its public statements.
Customers using affected certificates should follow the company’s official instructions and ensure that replacement certificates are installed correctly. Website operators should also check their certificate chains and confirm that browsers and other clients recognise the replacements as trusted.
Organisations that depend on certificates for public-facing websites or critical services should avoid waiting until a certificate fails unexpectedly. A planned transition can help minimise disruption and reduce the risk of security warnings for visitors.
Market reaction and the road ahead
The security incident also affected investor sentiment. Reuters reported that eMudhra shares fell around 40% over two days following disclosure of the vulnerability. The decline reflected concerns about reputational damage and the company’s response to the incident, even though the affected business represented a relatively small share of revenue.
The longer-term consequences will depend on the company’s ability to complete the withdrawal responsibly, demonstrate the effectiveness of its remediation measures and maintain confidence in its remaining services.
For the wider technology industry, the episode is a reminder that digital trust depends not only on strong encryption algorithms but also on sound implementation, rigorous key-generation procedures, independent scrutiny and transparent incident response.
eMudhra’s exit from the global TLS certificate business may reduce its exposure to a costly and increasingly complex segment. Nevertheless, the incident underscores the importance of maintaining reliable security practices across the digital infrastructure on which businesses, governments and internet users depend.